


Why Do DDoS Attacks Happen? 9 Common Motivations Explained

Effective DDoS defence starts with understanding why your organisation is being targeted. A spike in traffic tells you what is happening, but not necessarily who is behind it or what they want to achieve. Understanding the motivation behind an attack can provide critical context for incident response, threat assessment, and defence strategy.
DDoS attacks serve a range of purposes, from political protest and financial extortion to competitive sabotage and concealing other malicious activity. Here are nine common motivations behind modern DDoS campaigns and what they mean for your organisation.
The Main Motivations Behind DDoS Attacks

1. Hacktivism
Attackers target websites and online services to protest political, social, or ideological causes, or to retaliate against organisations whose actions they oppose. The primary goal is visibility and pressure rather than financial gain. These campaigns often coincide with major political events, geopolitical developments, or controversial corporate decisions.
2. Competition
A competitor, or someone acting on its behalf, launches a DDoS attack to cause downtime, disrupt operations, or drive customers towards an alternative service. Attacks may be timed to coincide with critical business periods, such as product launches, major sales, or high-profile events. This motivation is particularly relevant to sectors where service availability directly affects revenue, including gaming, e-commerce, and online gambling. For example, here’s a case study describing a DDoS attack on a gaming company.
3. Ransom
Attackers threaten to launch a DDoS attack, or begin one as a demonstration, and demand payment to stop the attack or prevent further disruption. Demands often come with strict deadlines and escalating threats. Organisations that depend heavily on online availability may be particularly attractive targets. For example, this case study describes how we handled a DDoS Ransom Attack on a Bank.
4. Cyber Warfare
Nation-states and state-sponsored groups may use DDoS attacks to disrupt government services, media organisations, military-related systems, or critical infrastructure as part of a broader geopolitical campaign. These attacks can coincide with diplomatic tensions, military operations, or other international developments. For targeted organisations, the risk may persist beyond a single incident. Here’s an example where our team uncovered DDoS protection gaps in time for elections.
5. Angry Customers
Disgruntled customers or users may launch attacks in response to a negative experience, such as an account ban, billing dispute, or unsatisfactory customer support. These attacks are often impulsive and limited in scope. However, inexpensive DDoS-for-hire services, commonly known as booter or stresser services, have lowered the barrier to launching disruptive attacks.
6. Angry Employees and Insiders
Current or former employees may use their knowledge of an organisation’s infrastructure to disrupt its services. Familiarity with internal systems, critical dependencies, and potential weaknesses can make these attacks more targeted than opportunistic traffic floods. Insider-driven incidents can also be harder to anticipate because the attacker may understand how the organisation’s defences and escalation procedures work.
7. Denial of Service as the Primary Objective
Sometimes, the objective is simply to make a service unavailable. Attackers seek to exhaust network bandwidth, connection capacity, or application resources, preventing legitimate users from accessing the service. The motivation behind the disruption may vary, but the operational impact can be immediate: lost revenue, degraded customer experience, and interruption to critical business processes.
8. The Smoke Screen: Concealing Another Attack
A DDoS attack can serve as a diversion, drawing security teams’ attention and consuming their resources while a separate attack takes place. Under cover of the disruption, attackers may attempt to steal data, deploy malware, or commit financial fraud.
In these cases, restoring service is only part of the response. Security teams must also determine whether the DDoS activity coincided with other suspicious events and investigate whether the incident was used to conceal a broader intrusion.
9. Security Denial of Service
Some attacks target the security infrastructure itself, rather than-or in addition to-the services it protects. Firewalls, web application firewalls (WAFs), intrusion prevention systems and logging platforms may be targeted or overwhelmed, potentially degrading their performance or visibility.
The consequences can extend beyond service availability. If a security control fails or monitoring becomes impaired, the organisation may lose visibility into other malicious activity or find that its protective measures are no longer operating as intended. The actual impact depends on the architecture, configuration and failover behaviour of the affected controls.
Final Thoughts: Align Your DDoS Defences with Your Threat Profile
The key question is not simply whether your organisation could be hit by a DDoS attack, but which types of attacks it is most likely to face and what the consequences would be.
Your exposure depends on factors such as your industry, geographic footprint, public profile, business model and dependence on online services. An organisation associated with a geopolitical conflict may face a heightened risk of hacktivist campaigns or state-linked disruption. A gaming company launching a major title, or a retailer preparing for Black Friday, may be more exposed to competitive sabotage and extortion attempts.
Understanding these risks helps security teams prioritise scenarios, assess the effectiveness of existing controls and prepare appropriate incident response procedures.
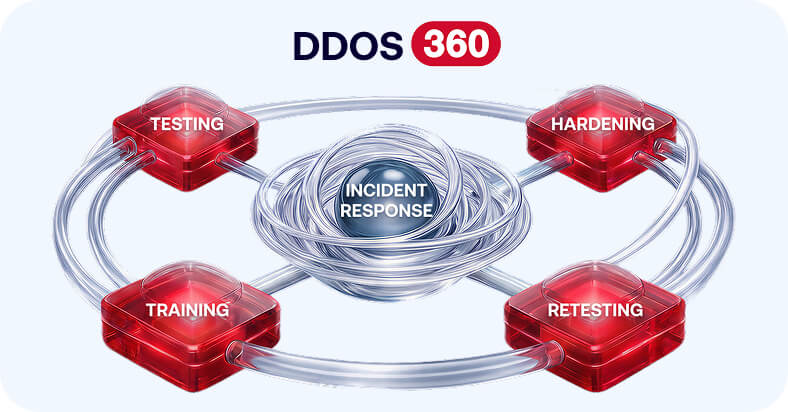
Buying a mitigation service and configuring traffic thresholds are not enough to establish resilience. Organisations also need to understand how their defences perform under realistic attack conditions, whether critical services remain available, and whether security and monitoring controls continue to function as expected.
The time to discover a gap in your DDoS defences is before an attack, not during one. By aligning your testing and response plans with your organisation’s actual threat profile, you can identify weaknesses, validate your controls and make better-informed decisions when an attack occurs.
Frequently Asked Questions About DDoS Attack Motivations
1. Why do hackers launch DDoS attacks?
Hackers launch DDoS attacks for various reasons, including financial extortion, political activism, competitive sabotage, revenge, and disruption of online services. Some attacks are also used to distract security teams while other malicious activities take place. Understanding the attacker’s potential motivation helps organisations assess threats and prioritise their defences, although motivation cannot always be determined from traffic patterns alone.
2. Can a DDoS attack be used to hide a data breach?
Yes. Attackers may use a DDoS attack as a diversion while attempting data theft, malware deployment or unauthorised access elsewhere in the organisation’s infrastructure. However, a DDoS attack does not necessarily indicate a data breach. Security teams should investigate suspicious activity across their systems during and after an attack, rather than focusing exclusively on restoring service availability.
3. How can organisations prepare for different DDoS attack motivations?
Organisations should assess their threat profile based on factors such as industry, geographic exposure, public visibility and dependence on online services. This assessment can guide incident response planning and help identify realistic attack scenarios. Regular DDoS testing can then validate whether existing protections, critical services, and monitoring systems perform as expected under those conditions.
About the author