

Volumetric Attacks
Our testing leverages a repository of over 100 attack vectors, combining multiple techniques to simulate real-world attack patterns.
Red Button simulates advanced attack vectors to uncover every DDoS vulnerability before it impacts your uptime.
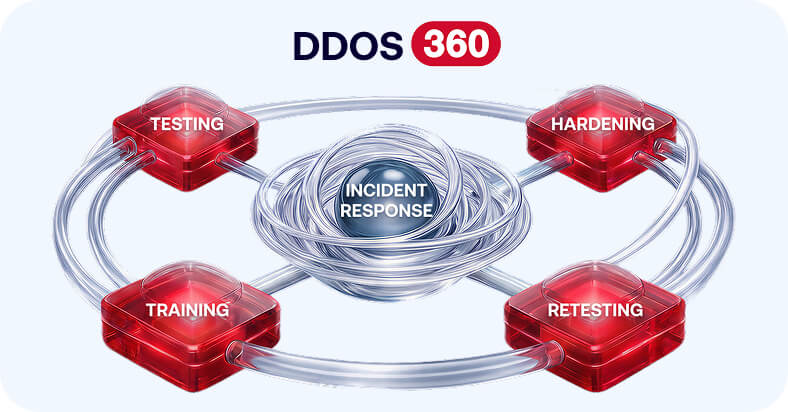
Our managed DDoS testing service works in full collaboration with your team, moving at your pace to ensure a controlled process and provide a detailed security audit and professional remediation roadmap.




We combine deep expertise, authorized execution, and advanced simulation capabilities to deliver meaningful results.

Authorized &
Safe
As an official testing partner for AWS and Azure, we can simulate real attack traffic without risking service disruption or violating provider policies. Read more about our AWS and Azure DDoS expertise.

Expert-Led Managed Service
Every engagement is designed and executed by experienced DDoS specialists who understand modern attack techniques and defense mechanisms.

Realistic Attack
Simulation
We tailor attack scenarios to your infrastructure, APIs, and traffic patterns—replicating how real attackers would target your environment.

Actionable
Outcomes
You don’t just get data—you get clear findings and prioritized remediation guidance that improves your security posture.
Detailed Audit Report: A full breakdown of how the DDoS testing was performed, covering attack impact and every identified DDoS vulnerability.
A standardized benchmark to quantify your current defensive posture.
Prioritized, actionable recommendations to harden your WAF, network, and cloud configurations.
A follow-up session to re-execute attacks and verify that your fixes successfully closed every DDoS vulnerability.

Volumetric Attacks
Our testing leverages a repository of over 100 attack vectors, combining multiple techniques to simulate real-world attack patterns.
Protocol Attacks
Exploitation of weaknesses in network and transport layers (e.g., SYN floods, TCP anomalies, fragmentation)
Application Layer Attacks
Targeted attacks on web applications and APIs (e.g., HTTP floods, slow attacks, TLS exhaustion)
No two environments are the same—and neither are our tests. Every engagement is customized based on:
This ensures the testing is relevant, realistic, and aligned with real-world threats.
Scoping comes before any traffic is generated: which assets are in scope, which protection layers sit in front of them, which vectors are realistic against that architecture, and what the business cannot afford to have happen during the test.
The reason this matters is that a standard script tests what every environment has in common, and the findings that hurt are almost always in what makes yours different.

Minimize
Downtime
Every minute of an attack costs revenue and brand trust.

Identify Hidden
Gaps
Uncover "low and slow" attacks that bypass traditional volume-based filters.

Verify
Defenses
Ensure your WAF, scrubbing centers, and firewalls are correctly configured whether it's on AWS, Azure or On-Prem infrastructure.

Compliance &
Standards
Align with OWASP, PTES, and WASC standards.
A test is built not to. Before anything runs, the test plan fixes the traffic volumes, the ramp-up rate and the abort conditions, and your team approves it. During the test, intensity rises in controlled increments. Our engineers stay on a live call with your team, and either side can trigger an emergency stop that halts traffic immediately. Most tests run off-peak or inside an agreed maintenance window, and they can target a non-production environment instead. The residual risk is not zero, and we go through it with you during planning. If a test exposes a weakness that affects service, we stop, and the report records the event with the fix.
For most enterprises, the minimum is once a year. For financial services, gaming, healthcare, government and critical infrastructure, we recommend testing quarterly. Run a test outside that cycle whenever your network architecture changes significantly. A migration, a new protection layer or a new internet-facing service can each move a threshold that the last test validated. After remediation, a targeted retest confirms that the gaps from the previous test are closed.
Yes. Verifying third-party mitigation services is a core part of our work, alongside on-premises appliances. A WAF that is deployed and configured is not the same as one that stops an application-layer flood at the threshold you expect. The test shows which rules trigger, which don’t, and where attack traffic gets through. We are vendor-neutral: the report covers how your configuration behaved under attack, not which product to buy. If the provider requires notice or approval before testing, we handle it during planning.
Yes. We generate attack traffic from legally acquired public cloud resources and dedicated, legitimate IP addresses. It reaches your infrastructure the way real attack traffic would, through the same ISP, CDN and scrubbing layers. No agent or appliance goes into your network. From your side, we need a named contact who can stop the test at any moment, plus access to your own monitoring during the test window. That comes to about five hours of your team’s time: a one-hour pre-test interview, the three-hour live session and a one-hour results readout.