

Volumetric Attacks
Our testing leverages a repository of over 100 attack vectors, combining multiple techniques to simulate real-world attack patterns.
Red Button simulates advanced attack vectors to uncover every DDoS vulnerability before it impacts your uptime.
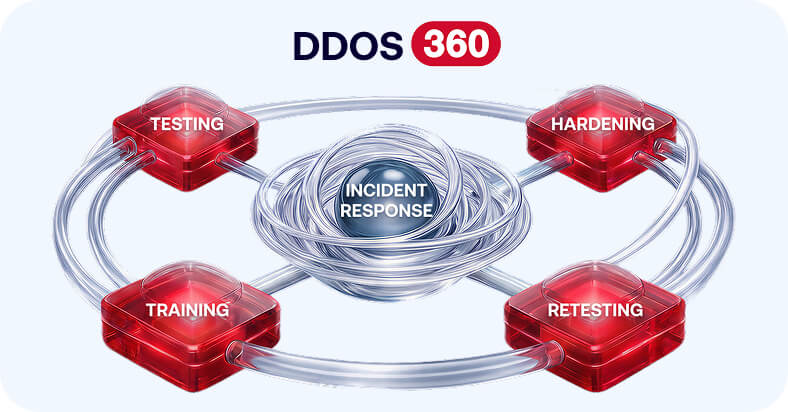
Our managed DDoS testing service works in full collaboration with your team, moving at your pace to ensure a controlled process and provide a detailed security audit and professional remediation roadmap.




We combine deep expertise, authorized execution, and advanced simulation capabilities to deliver meaningful results.

Authorized &
Safe
As an official testing partner for AWS and Azure, we can simulate real attack traffic without risking service disruption or violating provider policies. Read more about our AWS and Azure DDoS expertise.

Expert-Led Managed Service
Every engagement is designed and executed by experienced DDoS specialists who understand modern attack techniques and defense mechanisms.

Realistic Attack
Simulation
We tailor attack scenarios to your infrastructure, APIs, and traffic patterns—replicating how real attackers would target your environment.

Actionable
Outcomes
You don’t just get data—you get clear findings and prioritized remediation guidance that improves your security posture.
Detailed Audit Report: A full breakdown of how the DDoS testing was performed, covering attack impact and every identified DDoS vulnerability.
A standardized benchmark to quantify your current defensive posture.
Prioritized, actionable recommendations to harden your WAF, network, and cloud configurations.
A follow-up session to re-execute attacks and verify that your fixes successfully closed every DDoS vulnerability.

Volumetric Attacks
Our testing leverages a repository of over 100 attack vectors, combining multiple techniques to simulate real-world attack patterns.
Protocol Attacks
Exploitation of weaknesses in network and transport layers (e.g., SYN floods, TCP anomalies, fragmentation)
Application Layer Attacks
Targeted attacks on web applications and APIs (e.g., HTTP floods, slow attacks, TLS exhaustion)
No two environments are the same—and neither are our tests. Every engagement is customized based on:
This ensures the testing is relevant, realistic, and aligned with real-world threats.
Scoping comes before any traffic is generated: which assets are in scope, which protection layers sit in front of them, which vectors are realistic against that architecture, and what the business cannot afford to have happen during the test.
The reason this matters is that a standard script tests what every environment has in common, and the findings that hurt are almost always in what makes yours different.

Minimize
Downtime
Every minute of an attack costs revenue and brand trust.

Identify Hidden
Gaps
Uncover "low and slow" attacks that bypass traditional volume-based filters.

Verify
Defenses
Ensure your WAF, scrubbing centers, and firewalls are correctly configured whether it's on AWS, Azure or On-Prem infrastructure.

Compliance &
Standards
Align with OWASP, PTES, and WASC standards.
No. Our experts coordinate testing during off-peak hours and use controlled increments to ensure no unintended outages.
We recommend quarterly audits or whenever significant changes are made to your network architecture.
Yes, we specialize in verifying the effectiveness of third-party mitigation services and local appliances.
Yes. Attack traffic is generated from legally acquired public cloud resources and dedicated legitimate IP addresses, and arrives at your estate the way real traffic does – so there is no agent and no appliance to install in your network. What we ask from you is a named contact who can stop the test at any moment, and access to your own monitoring during the window so that both sides are watching the same event.